Admin, OIDC, SLA, and compliance
Workspace administration lives in Workbench Admin and Compliance. These are cloud workspace areas, not local files.
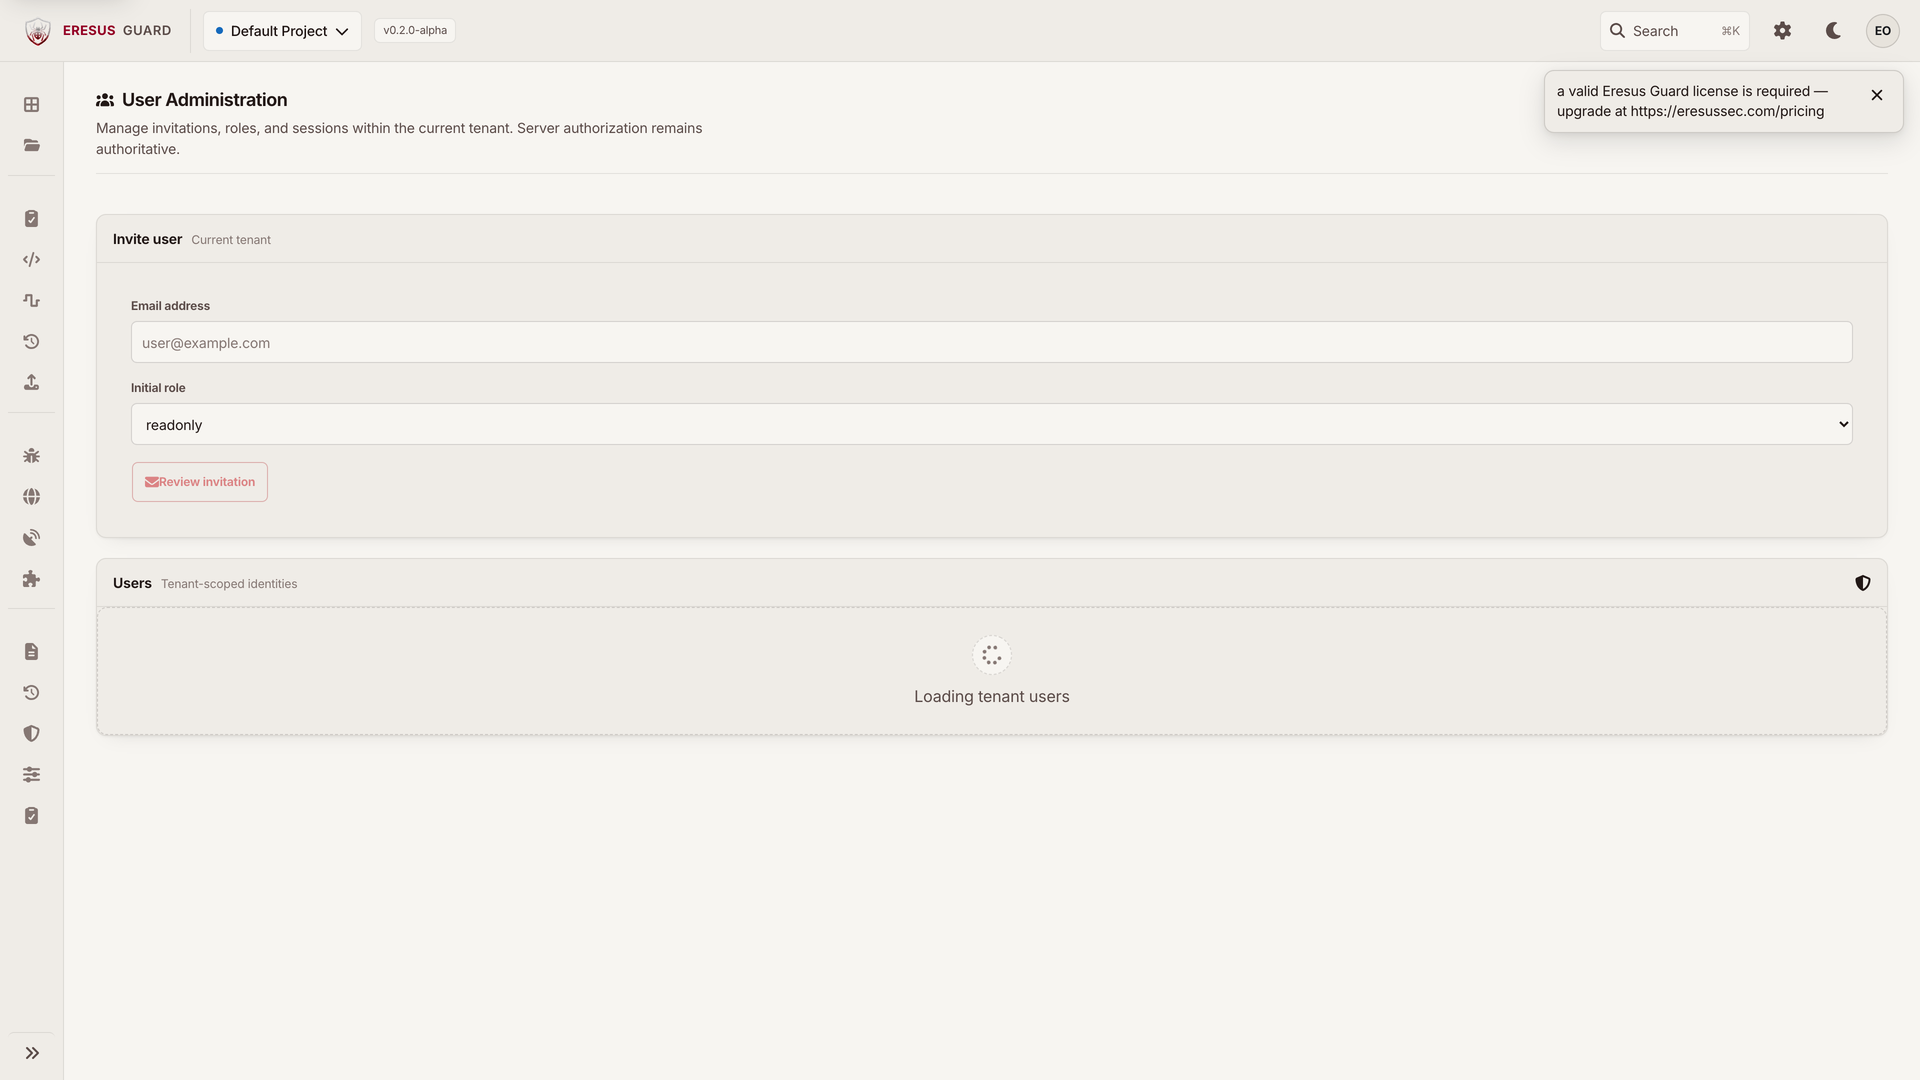
Users
Administrators invite, assign, and remove users in Admin. Roles decide who can open projects, start scans, triage findings, and export evidence.
Do not share Workbench sessions. Each operator should have their own user.
OIDC
OIDC is configured in Admin for organization SSO. After it is enabled, users authenticate with the identity provider and land in Workbench.
OIDC does not grant extra project scope. Project authorization is still explicit.
SLA
SLA settings belong to the workspace plan. Use Admin to see the service-level terms that apply to the provisioned tier. SLA is not configured from the CLI.
Compliance
Compliance views stay attached to the same projects and evidence trail. Use them to review control-oriented output without exporting the entire HTTP corpus.
Restrict who can open Compliance. The views can still contain sensitive routes, identities, and evidence references.
Related
Need a workflow that is not documented here? Email contact@eresussec.com.