Bring the API definition, request, or traffic you already have.
Eresus Workbench accepts authorized API inputs and keeps the resulting assessment in the same project as the target, findings, and evidence reviewers need to verify it.
Start from the API material that best represents the system.
Use a URL, URL list, cURL input, captured Burp request and response, OpenAPI definition, or Postman collection. The ingest path is an input to a scoped assessment, not a way to discover unapproved systems.
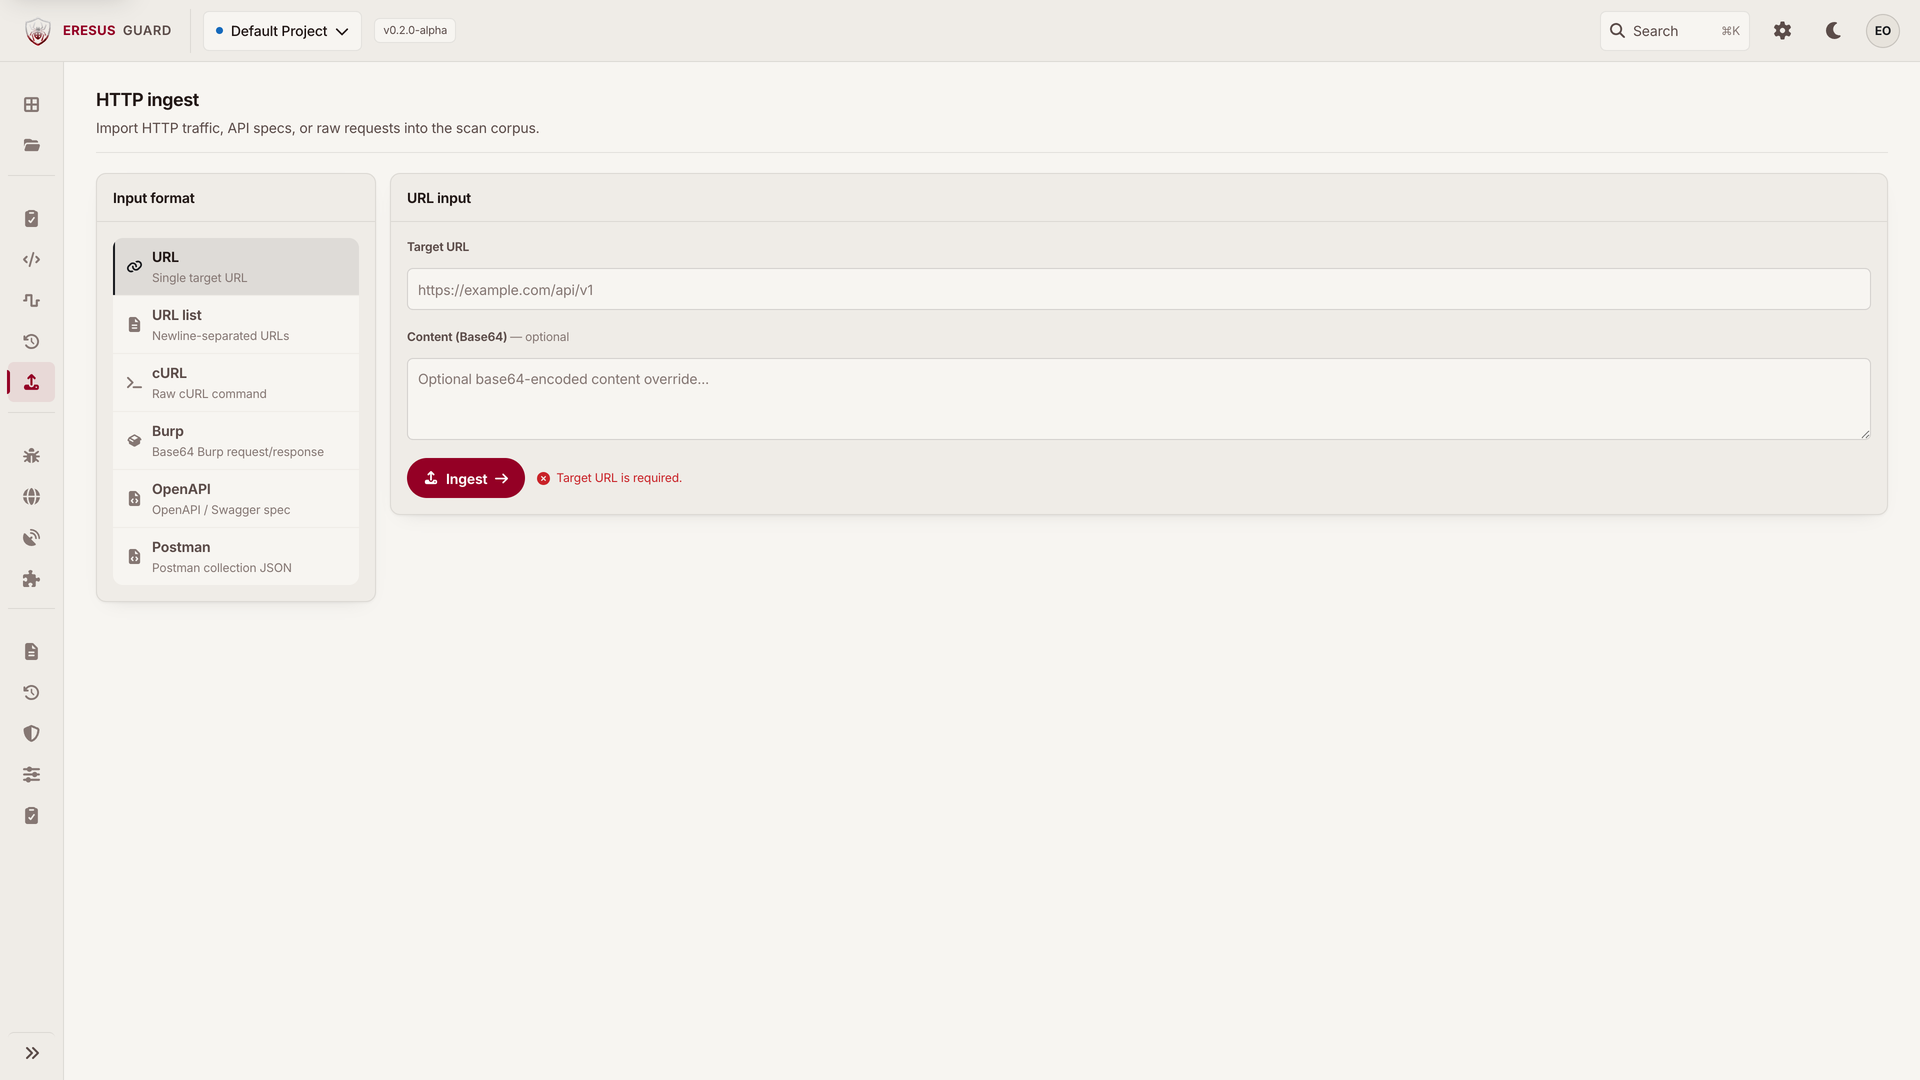
Keep API findings connected to the request that demonstrated them.
API security review is faster when a finding does not have to be reconstructed from a detached report. Workbench retains HTTP records with the project so engineering and security can inspect the same evidence before a retest.
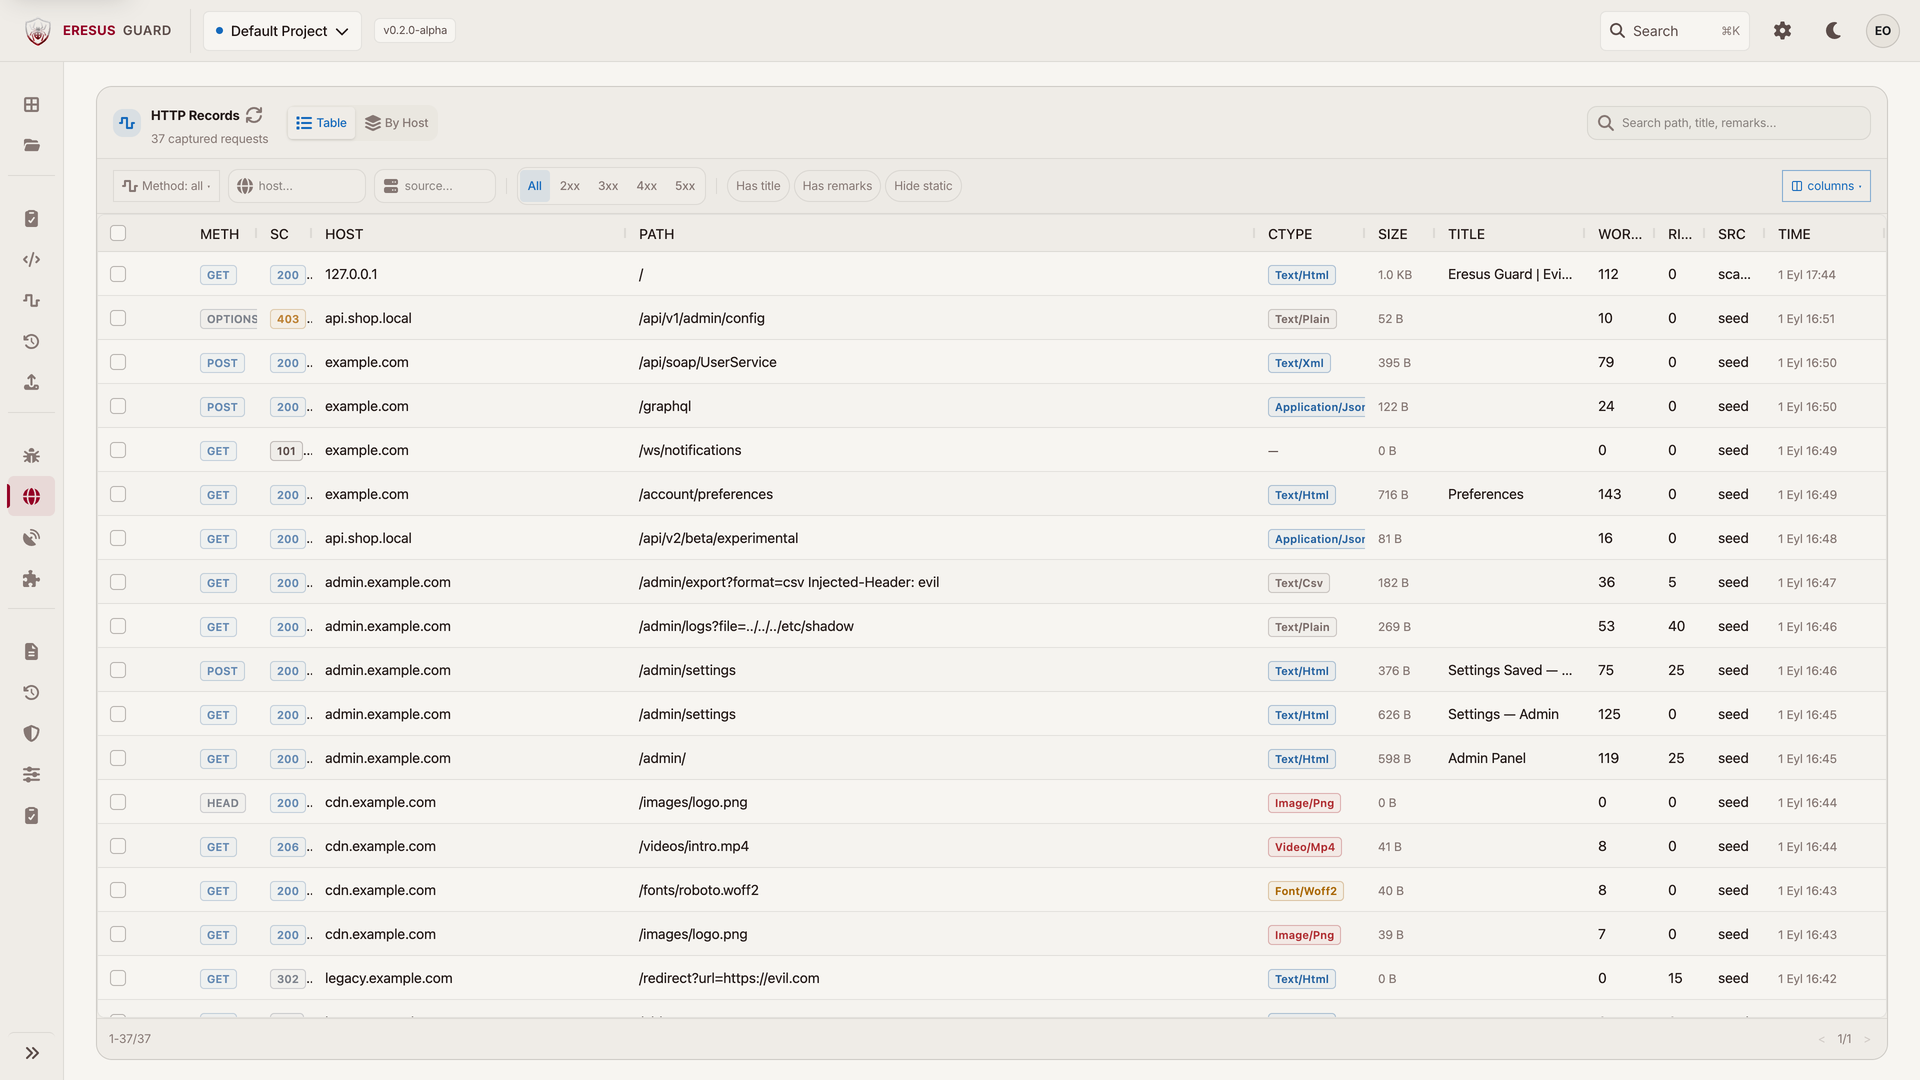
Three steps from approved scope to a reviewable result.
- 1
Add an authorized API input to the project.
- 2
Set scope and authentication before the assessment runs.
- 3
Review HTTP evidence, export results, and verify the remediation.